Introduction
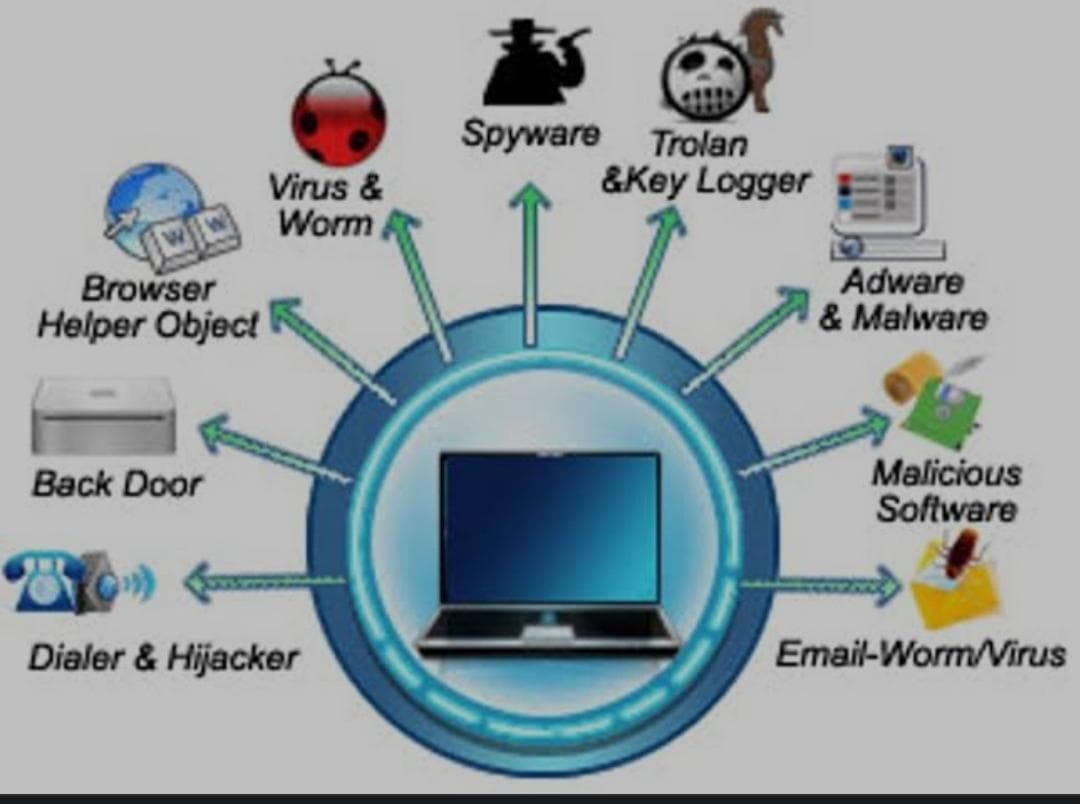
In today's interconnected world, data is the lifeblood of businesses and individuals alike. The efficient transfer of information over networks is essential for communication, productivity, and innovation. However, the same networks that facilitate data transfer can also be vulnerable to threats if not properly secured. Network sniffing is one such threat, and it involves eavesdropping on data packets as they traverse a network. This article explores network sniffing techniques, its implications, and how to defend against it.
Understanding Network Sniffing
Network sniffing is the practice of intercepting and monitoring data packets as they travel across a network. This process is typically carried out by hackers or network administrators for legitimate purposes like troubleshooting and monitoring network performance. However, it can also be used maliciously to steal sensitive information, such as login credentials, financial data, or intellectual property.
Network sniffing works by capturing data packets as they move between devices on a network. These packets contain information like source and destination addresses, data payload, and protocols used. By analyzing this information, attackers can gain insights into the network's structure and identify potential vulnerabilities.
Common Network Sniffing Techniques
- Packet Sniffing Tools: Hackers often use specialized software tools like Wireshark, tcpdump, or Cain and Abel to capture and analyze network traffic. These tools allow them to see the data being transmitted in real-time.
- ARP Spoofing: Address Resolution Protocol (ARP) spoofing involves tricking devices on a network into sending their data to the attacker's machine instead of the intended recipient. This enables the attacker to intercept and analyze the traffic.
- Promiscuous Mode: Network interface cards (NICs) can be put into promiscuous mode, allowing them to capture all network traffic, not just packets intended for the specific device. This mode is often used by legitimate network administrators but can also be exploited by attackers.
- Port Mirroring: In enterprise environments, network administrators may set up port mirroring to monitor network traffic for security or performance analysis. If an attacker gains access to these mirrored ports, they can intercept network data.
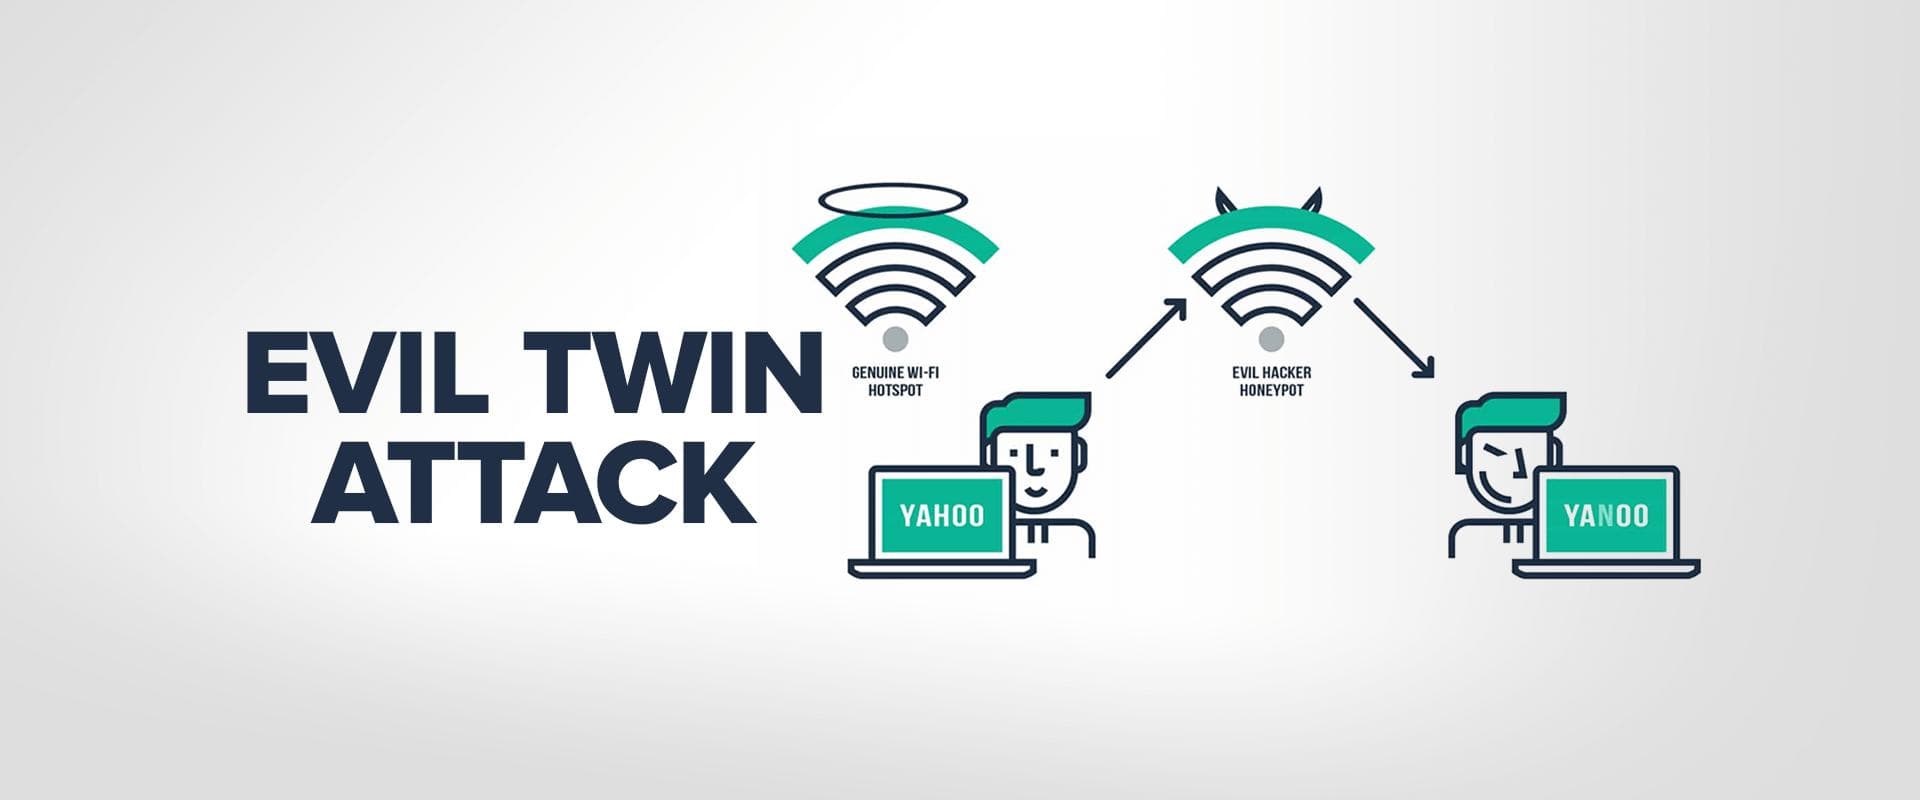
- Man-in-the-Middle (MitM) Attacks: In a MitM attack, the attacker positions themselves between the communication path of two parties and intercepts their data. This can be done through techniques like ARP spoofing or DNS hijacking.
Implications of Network Sniffing:
The implications of network sniffing can be severe:
- Data Theft: Attackers can steal sensitive information, such as login credentials, credit card numbers, or confidential business data.
- Privacy Invasion: Network sniffing can compromise personal privacy, as it can intercept emails, chats, or any other data transmitted over the network.
- Data Manipulation: In some cases, attackers may alter data packets in transit, leading to data corruption or fraudulent activities.
- Network Vulnerability Discovery: Sniffing can help attackers identify weaknesses in a network's security, potentially leading to further attacks.
Defending Against Network Sniffing:
Protecting your network against sniffing attacks is crucial. Here are some key strategies:
- Encryption: Implement end-to-end encryption for sensitive data. Technologies like HTTPS, VPNs, and SSL/TLS make it difficult for attackers to decipher intercepted traffic.
- Network Segmentation: Divide your network into segments and restrict access between them. This limits the scope of potential sniffing attacks.
- Intrusion Detection and Prevention Systems (IDPS): Employ IDPS to detect and block suspicious network activity.
- Regular Updates and Patch Management: Keep all software, including network devices and security software, up to date with the latest security patches.
- User Training: Educate employees and users about the dangers of network sniffing and train them to recognize phishing attempts and other forms of attack.
- Monitoring and Logging: Continuously monitor network traffic and maintain detailed logs for analysis. This can help identify unusual activity.
Conclusion:
Network sniffing techniques pose a significant threat to the security and privacy of data transmitted over networks. While they can be used for legitimate purposes, they are equally accessible to malicious actors. Understanding these techniques and taking proactive measures to defend against them is essential in today's digital landscape. By implementing encryption, network segmentation, and a robust security posture, individuals and organizations can safeguard their data and maintain the confidentiality and integrity of their network communications.