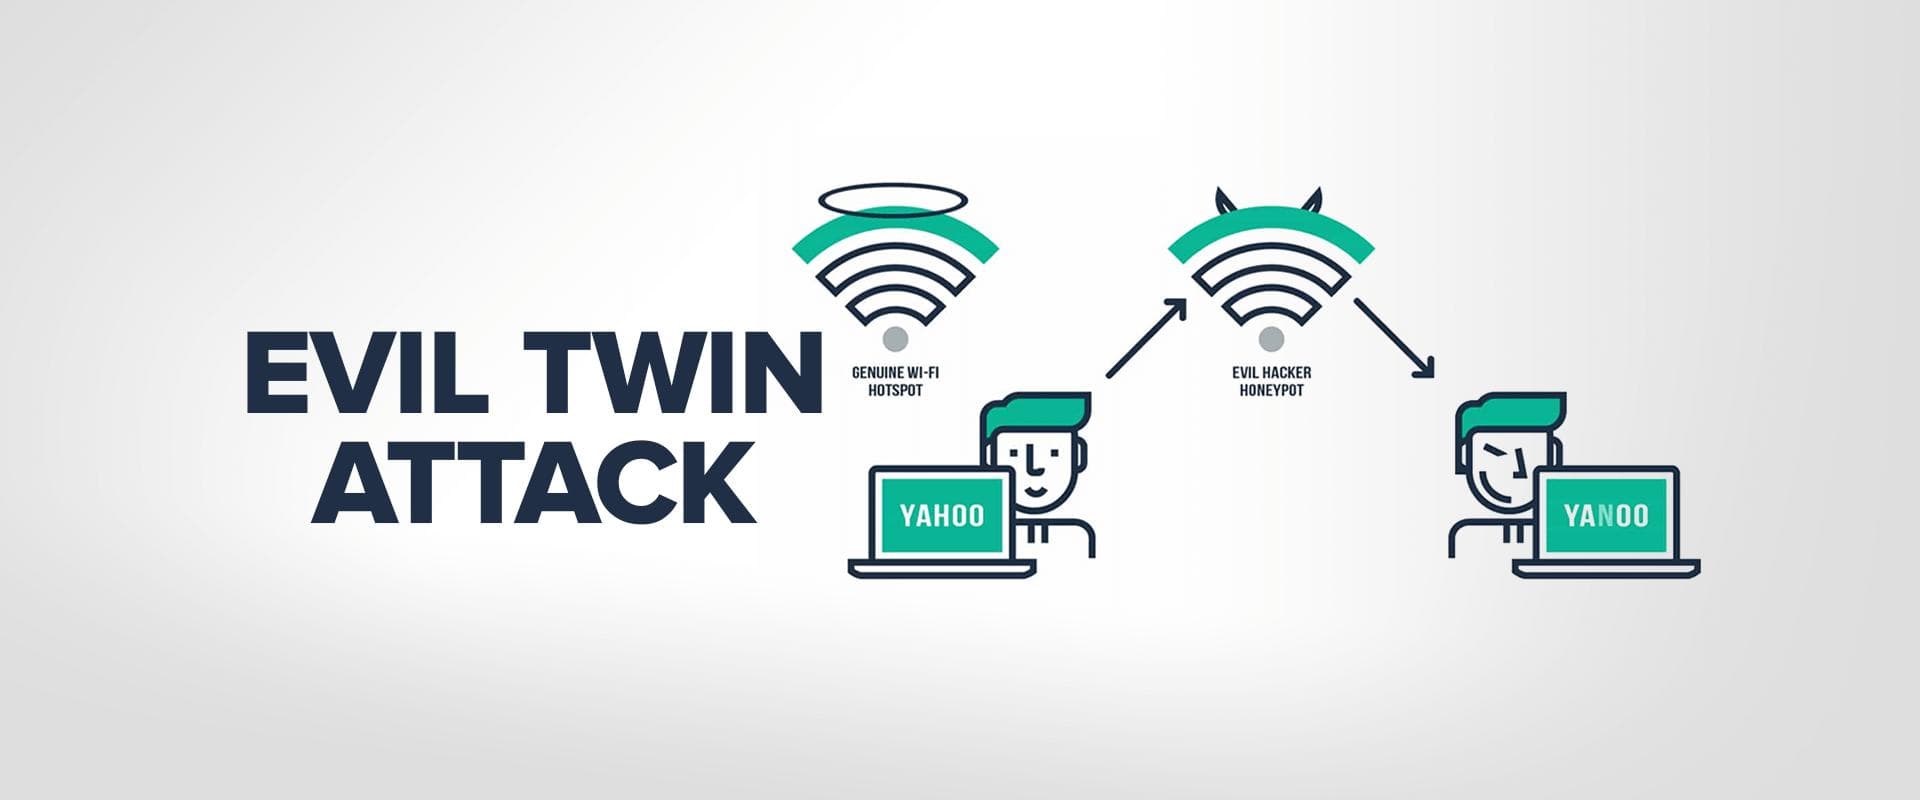
Payment Card Industry - Data Security Standard is an abbreviations(PCI-DSS) . Before 2004, major credit card brands such as American Express, MasterCard, Visa, Discover and JSB used to implement their own version of security programme. They collaborated together to create a universally accepted programme to encourage and improve cardholder data security.but due to this lot of data breach had happened cybercriminal activities has taken place .As a universal Standard, any merchant or service provider that stores,processes or transmits cardholder data is required to comply with this standard. Organizations that misses the mark to fulfill are ignored by the clients (after all, it’s all about their date), and those that undergo security breach and are found out to be out of compliant are possibly fined.But in 2006 the five card companies told to make some security standard council(SSC).PCI Security Standards Council (PCI SSC) It is a standarad not a law which set by security standard council in which the set rules or guidelines regarding Payment cards through banking and banking applications in between merchants and clients .where customers can easily make transaction online .In online banking appliactions adequate security testing to ensure card holder data is never compromised.Run controlled data breach attempts against the bank network on regular basis to ensure network, end-point and web application security.Perform security testing to detect well known vulnerabilities like SQL injection, OS command injection, Cross-site scripting, broken authentication etc.Test for the presence of authorized and un-authorized wireless access points on a quarterly basis.Perform penetration testing – white box and black box – on network layer and application layer at least once a year or after a signification change has been made to the application.Scope of penetration testing is the card holder environment (CDE) + systems and networks connected to it (unless the bank has a segmented network in which the CDE is isolated from other systems).Penetration testing should aim to identify all possible threats and vulnerabilities and try to exploit them to penetrate the system both at the application and network level.Issues identified should be corrected and re-tested until all chances of malicious activity are removed