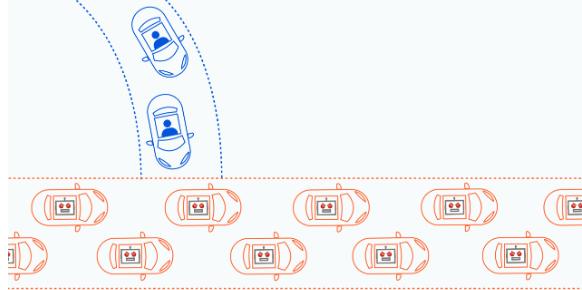
A DDoS attack floods a system or network with traffic from multiple compromised devices, disrupting normal operations and making it unavailable to genuine users. Strong cybersecurity measures are necessary to detect and prevent these attacks, which can cause downtime, financial losses, and damage to a target's reputation.
WHAT IS DISTRIBUTED DENIAL OF SERVICE?
A distributed denial-of-service (DDoS) attack is a malicious attempt to disrupt the normal traffic of a targeted server, service, or network by overwhelming the target or its surrounding infrastructure with a flood of Internet traffic. DDoS attacks achieve effectiveness by utilizing multiple compromised computer systems as sources of attack traffic.
HOW DOES A DDoS ATTACK WORK?
To carry out a DDoS attack, the attacker needs to control a large number of systems, which are called bots. These systems are often compromised by malware, which gives the attacker control over the system. The attacker then uses these systems to send traffic to the target system.
The amount of traffic that can be generated by a DDoS attack can be very large. For example, a single botnet that was used in a 2016 attack was able to generate 1.7 terabits per second of traffic. This is enough to overwhelm most websites and servers.
HOW TO IDENTIFY THE DDoS ATTACK?
1. Sudden spikes in traffic: If you see a sudden and unexplained increase in traffic to your website or server, it could be a sign of a DDoS attack.
2. Slow performance: If your website or server is suddenly slow or unresponsive, it could be a sign of a DDoS attack.
3. Errors: If you are seeing errors on your website or server, such as 503 errors or connection refused errors, it could be a sign of a DDoS attack.
4. Abnormal network activity: If you see abnormal network activity, such as a large number of connections from a single IP address or a large number of connections from a specific country, it could be a sign of a DDoS attack.
5. Complaints from users: If you are receiving complaints from users that they are unable to access your website or server, it could be a sign of a DDoS attack.
COMMON TYPES OF DDoS TYPES
1. Application layer attacks
The application layer is where the server generates the response to an incoming client request.
For example, if a user enters http://www.xyz.com/learning/ on their browser, an HTTP request is sent to the server. The server will fetch all the information related to the page, package it in a response, and send it back to the browser.
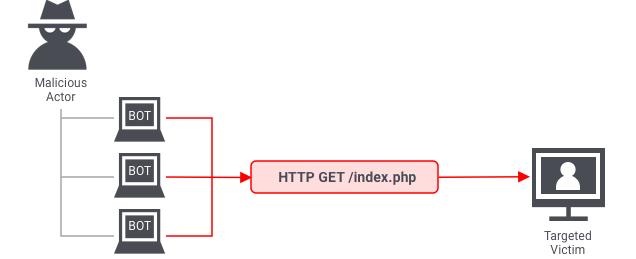
An application layer attack occurs when a hacker uses different bots/machines to repeatedly request the same resource from the server, eventually overwhelming it.
The most common type of application layer attack is the HTTP flood attack in which malicious actors just keep sending various HTTP requests to a server using different IP addresses.
2. Protocol attacks
Protocol attacks look to exhaust the sources of a server or those of its networking systems like firewalls, routing engines, or load-balancers. An example of a protocol attack is the SYN flood attack.
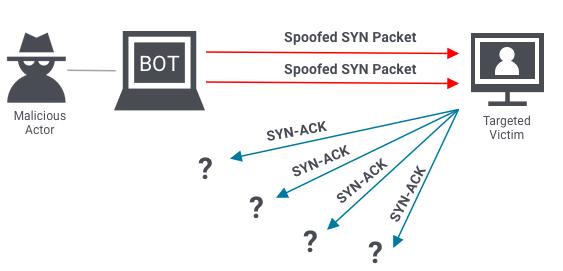
Before two computers can initiate a secure communication channel – they must perform a TCP handshake. A TCP handshake is a means for two parties to exchange preliminary information. A SYN packet is typically the first step of the TCP handshake, indicating to the server that the client wants to start a new channel.
In a SYN flood attack, the attacker floods the server with numerous SYN packets, each containing spoofed IP addresses. The server responds to each packet (via SYN-ACKs), requesting the client to complete the handshake. However, the client(s) never respond, and the server keeps waiting. Eventually, it crashes after waiting too long for too many responses.
3. Volumetric attacks
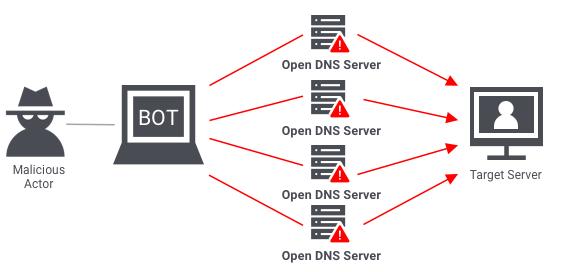
Volumetric attacks are conducted by bombarding a server with so much traffic that its bandwidth gets completely exhausted. The most common example of a volumetric attack is the DNS amplification attack.
In such an attack, a malicious actor sends requests to a DNS server, using the spoofed IP address of the target. The DNS server then sends its response to the target server. When done at scale, the dedeluge ofNS responses can wreak havoc on the target server.
Preventing DDoS Attack
Real-time packet analysis: Analyze packets based on different rules, as they enter your system, discarding the potentially malicious ones.
DDoS defense system (DDS): A DDS can detect legitimate-looking content with malicious intent. It protects against both protocol and volumetric attacks, without requiring any human intervention.
Web application firewall: Web application firewalls (WAF) are a great tool to mitigate application layer DDoS attacks. They give you a way to filter incoming requests, based on different rules, which can also be added on-the-fly, in response to an attack.
Rate limiting: Limit the number of requests a server can entertain over a certain time period.